Why effective cybersecurity is important for businesses

Why effective cybersecurity is important for businesses

Cyber attacks can have serious financial and business consequences for companies, which makes implementing strong cybersecurity protections a critical step.

The threat of a successful cyber attack ranks as one of the most significant business risks organizations of all sizes and across all industries face. Business and IT executives have good reason to rate cyberthreats as a high-level risk — and to invest in a strong cybersecurity program for their company.

The volume and sophistication of cyber attacks have grown significantly since the first computer viruses emerged in the 1970s and the Morris worm became the first major internet-based attack in 1988. Moreover, the number of devices connected to the internet and corporate networks exploded during the past few decades. The reliance on IT systems for everyday business tasks also spiked in recent years, driven partly by digital transformation initiatives in companies.

Consequently, a single successful attack can have a catastrophic impact, with the potential to expose personal information, bring a company’s operations to a halt, cripple critical infrastructure and even physically harm people.

Recognizing the importance of cybersecurity, enterprise leaders in many organizations have increasingly prioritized it, seeking to implement more rigorous policies, procedures and technologies to defend against cyberthreats of all kinds — data breaches, ransomware attacks, phishing and more.

This article is part of

The ultimate guide to cybersecurity planning for businesses

For instance, the “2024 Focus on the Future” report from software vendor AuditBoard identified cybersecurity and data security as the No. 1 risk category among surveyed risk management and internal audit executives for the third year in a row. More than 80% of the 453 respondents also put it in the top spot for expected audit efforts in 2024. Similarly, professional services firm PwC’s “2024 Global Digital Trust Insights” survey found that mitigating cyber-risk was second on the priority list among the 3,876 business and IT executives who responded, outranked only by managing digital and technology risks.

Such viewpoints are pushing up cybersecurity budgets. Consulting and market research firm Gartner projected that combined spending on security and risk management by user organizations worldwide will total $215 billion in 2024, a 14.3% increase over the $188.1 billion it estimated for 2023.

Why strong cybersecurity is critical to business success

The following factors show why effective cybersecurity is seen as a necessary part of doing business:

  1. Nearly every organization requires IT systems to function, which has significantly increased the consequences of a successful cyber attack. “We have become so dependent on technology that the majority of businesses cannot operate without it,” said Carl Eyler, director of the National Cybersecurity Institute at Excelsior University, an online school based in Albany, N.Y.
  2. Data is now one of the most valuable assets — often the single most valuable one — in most companies. Any security issues that hurt an organization’s data quality or access could affect business operations.
  3. Cybercrime continues to grow in nearly every way. The number of bad actors is increasing, as are the sophistication of their attacks and the access they have to tools and technologies to help launch those attacks. As an example, the growing availability of ransomware as a service and other as-a-service malware has made it easier for attackers to strike, said Sarb Sembhi, a member of the Emerging Trends Working Group at professional association ISACA and CTO of Virtually Informed Ltd. Google Cloud’s “Cybersecurity Forecast 2024” report made similar points, warning among other things that attackers are using AI to their advantage and that new trends in malware development are making it faster to create and harder to detect.
  4. Government regulations and industry requirements mandate cybersecurity standards for many businesses, giving them no choice in making cybersecurity a priority. The U.S., individual states, the EU and other governments all have laws requiring organizations to safeguard sensitive data and implement prescribed cybersecurity practices. For example, the U.S. Securities and Exchange Commission in July 2023 adopted rules requiring all companies that file registration statements for stock offerings to disclose “material cybersecurity incidents” and to annually submit information on their cybersecurity strategy, governance and risk management initiatives. A case in point on industry mandates is PCI DSS, which sets standard security policies and procedures for any entity that accepts payment cards.
  5. Many consumers and business partners now have higher expectations that companies will make the necessary cybersecurity investments to thwart cybercriminals from stealing customer information and doing anything else that could harm customers and partners by extension. Meeting those demands presents business opportunities. “Creating and building trust with customers can be translated into revenue gains,” said Erik Avakian, a technical counselor at Info-Tech Research Group and former state CISO for the Commonwealth of Pennsylvania.

Cybercrime’s business costs and consequences

The numbers on the costs of cybercrime are staggering. Here are some overall figures:

  • The average cost of a data breach among 553 organizations worldwide was $4.45 million, according to IBM’s “Cost of a Data Breach Report 2023,” which was based on a study by research firm Ponemon Institute that examined breaches occurring between March 2022 and March 2023. That was an all-time high for the annual report and amounted to a 2% increase from the year before and a 15% one from the 2020 level.
  • Almost identically, PwC’s digital trust survey found that the average cost of a damaging cyber attack was $4.4 million, with 36% of respondents reporting that their organization had been hit by a data breach with an estimated cost of more than $1 million in the past three years.
  • An early 2023 survey found that the average ransom payment in response to a successful ransomware attack during the previous 12 months was $1.54 million, according to “The State of Ransomware 2023,” a report from cybersecurity software vendor Sophos, which commissioned the survey of 3,000 IT and cybersecurity professionals. That was nearly double the average payment of $812,380 in the 2022 version of the annual survey. In addition, the 2023 survey respondents reported an average of $1.82 million in estimated recovery costs, covering things such as downtime, people time, device costs and lost business opportunities.
  • The annual cost of cybercrime worldwide is expected to amount to $8.15 trillion for 2023 and increase to $13.82 trillion in 2028, according to predictions by market data and research firm Statista.

The list of cybersecurity incidents goes on and on. For example, a September 2023 ransomware attack on MGM Resorts International that used social engineering techniques to gain access to privileged user accounts cost the hospitality company an estimated $100 million and disrupted customer room access, casino games and other services. MGM said it expected its cybersecurity insurance policy to cover all the costs, but it also disclosed that the attackers stole personal information on some customers, including driver’s license, Social Security and passport numbers.

Caesars Entertainment was hit by a similar attack the same month. It paid a $15 million ransom, according to The Wall Street Journal, and likewise disclosed that the attackers obtained sensitive personal information on customers. In an SEC filing, Caesars said it took steps to “ensure that the stolen data is deleted by the unauthorized attacker, although we cannot guarantee this result.”

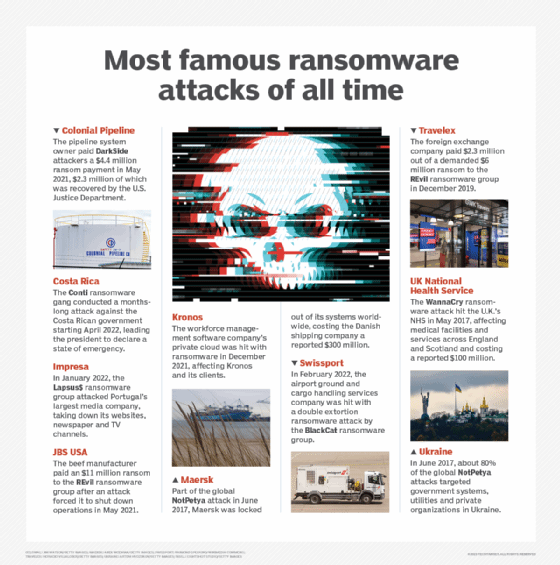
In another well-known example, a 2021 ransomware attack on Colonial Pipeline led to gas supply shortages in multiple U.S. states and cost the pipeline operator $4.4 million in ransom payments, some of which was later recovered by the U.S. Department of Justice. And Denmark-based shipping giant A.P. Moller-Maersk suffered upwards of $300 million in losses after a 2017 malware attack shut down the systems used to operate its shipping terminals around the world.

An organization that finds its cybersecurity defenses have been penetrated typically faces a long list of expenses as it seeks to repel the attack, restore affected systems and recover from the incident.

In addition to the required staff time, Eyler said organizations can expect to pay for outside technical support, inside and outside legal counsel, data breach notification costs and regulatory fines. They’ll also have costs due to lost sales and business opportunities. “You don’t know how far-reaching the costs are going to be when you’ve been breached,” he noted.

A company’s reputation with customers likely will also take a hit, which can translate into additional lost business in the future. Sembhi said the costs and consequences of an attack could even tank organizations — especially those without enough resources and reserves to weather the event’s aftermath. “With small businesses, one attack can take them out,” he warned.

10 well-known ransomware attacks
Here are details on 10 prominent ransomware attacks against organizations in various countries.

Business benefits of effective cybersecurity

The ramifications of cyber attacks have pushed many enterprise leaders — directors, CEOs, CFOs and other senior business executives, as well as CIOs and CISOs — to focus on improving their organization’s security posture.

For example, professional services firm Deloitte’s “2023 Global Future of Cyber Survey” found that 70% of more than 1,000 cybersecurity decision-makers said security issues were on their board’s agenda either monthly or quarterly. In addition, 86% said cybersecurity initiatives had made a significant contribution to at least one key business priority, including improvements in things such as customer trust, brand reputation and operational stability.

Such findings reflect a shift in thinking among executives who now see the cybersecurity program as an enabler of business operations, not merely a backstop for preventing losses.

“That’s the perspective companies have to have when it comes to cybersecurity,” said Fred Rica, a partner in the advisory practice at professional services firm BPM. “It allows them to do things they couldn’t do before, and it allows them to be more efficient, save money and be more productive.”

To illustrate the point, Rica cited the common business strategy of a company wanting to build a self-service portal for its customers. But that’s only feasible if the company has appropriate security measures to authenticate customers and is properly safeguarding their data, he said.

Key elements of a cybersecurity strategy

There’s no universal basis for what makes a strong cybersecurity program — each organization must determine its required level of security. To do so, Rica said companies should primarily think about whether their security efforts are appropriate from a business perspective.

That involves concepts such as risk appetite and risk tolerance and how much residual risk business executives are willing to accept. “If they’re comfortable that they’ve identified their risks, that those risks are managed and that the risks they’ve left on the table fit their risk profile, then they have a good program,” he said.

Organizations also must identify critical systems and assets and understand the particular cyberthreats they’re most likely to face, so they can invest in the right amount of people, processes and technology to mitigate security risks to an acceptable level, Avakian said. He added that developing a cybersecurity strategy is an ongoing exercise because “things change all the time.”

Other key elements of creating a successful cybersecurity strategy include the following:

  • Alignment with business goals.
  • Visibility into where data resides within the organization. “Understand where it is, who has access to it, what access controls are in place and the entry points to the data,” Eyler said.
  • An understanding of the security and data privacy laws with which the organization must comply.
  • A detailed cybersecurity risk assessment that evaluates the organization’s existing ability to protect itself from cyberthreats and identifies where its defenses fall short. “Measure where you have gaps and then decide what initiatives to put in place to close those gaps,” Avakian said.
  • A defined set of cybersecurity metrics for measuring how well the security program performs and how it improves over time.
  • A cybersecurity governance structure to ensure that employees adhere to established security policies and procedures.
  • Support and involvement from senior executives to help ensure that there’s adequate funding and high-level advocacy for the cybersecurity program.
  • A detailed incident response plan that’s regularly tested and practiced by both the security team and business units.

Tips on implementing and managing a cybersecurity program

The following best practices can help create an effective cybersecurity program:

  • Build a security-minded culture. Developing an internal culture that emphasizes cybersecurity is a must. “All stakeholders should know and understand what their responsibilities are from a cybersecurity perspective because security should be everybody’s job,” Eyler said.
  • Implement a comprehensive cybersecurity awareness and training program. To help foster a cybersecurity culture, all employees and relevant stakeholders should be trained on the importance of cybersecurity and the particular policies and procedures adopted by the organization.
  • Create cybersecurity champions. These are people throughout the organization who can evangelize the importance of following security policies and procedures. “Championing security starts with the CISO, but the CISO can’t do it all,” Avakian explained.
  • Focus on improving cybersecurity performance over time. “Every day should be about continuous improvement,” Avakian said.

Why UX & SEO Go Hand in Hand for Online Success

Why UX & SEO Go Hand in Hand for Online Success

In the ever-evolving digital landscape, businesses often treat Search Engine Optimization (SEO) and User Experience (UX) as separate disciplines. However, this siloed approach can significantly limit online success. The truth is that UX and SEO are deeply interconnected, with each enhancing the other when properly aligned. This comprehensive guide explores why UX and SEO should be considered two sides of the same coin and how their integration creates a powerful foundation for digital success.

The Evolving Relationship Between UX and SEO


Search engines have come a long way from the days when keyword stuffing and backlink quantity were the primary ranking factors. Today’s algorithms, particularly Google’s, have become increasingly sophisticated in evaluating websites based on how well they serve user needs. This evolution has created a natural convergence between SEO and UX.

Historical Perspective

Era SEO Focus UX Consideration Relationship
Early 2000s Keywords, meta tags, link quantity Minimal Disconnected
2010-2015 Content quality, natural language Page load speed, mobile compatibility Beginning to connect
2015-2020 User intent, dwell time Engagement, navigation, accessibility Strongly connected
2021-Present Page experience, core web vitals Holistic user journey, personalization Inseparable

As this timeline demonstrates, the relationship between these disciplines has evolved from completely separate concerns to intrinsically linked factors that determine online success.

How Google’s Algorithm Updates Prioritize User Experience

Google’s major algorithm updates have increasingly emphasized user experience factors as ranking signals:

  1. Mobile-Friendly Update (2015): Prioritized mobile-responsive websites in search rankings.
  2. RankBrain (2015): Introduced AI to better understand user intent and satisfaction.
  3. Speed Update (2018): Made page speed a ranking factor for mobile searches.
  4. Page Experience Update (2021): Incorporated Core Web Vitals metrics directly into ranking signals.
  5. Helpful Content Update (2022): Prioritized content that provides a satisfying experience and fulfills user expectations.

These updates clearly signal Google’s commitment to rewarding websites that prioritize positive user experiences.

Key UX Factors That Directly Impact SEO Performance

Key UX Factors That Directly Impact SEO Performance

1. Page Load Speed

Page speed affects both user experience and search rankings. Consider these statistics:

  • 53% of mobile users abandon sites that take longer than 3 seconds to load
  • A 1-second delay in page response can result in a 7% reduction in conversions
  • Pages that load within 2 seconds have an average bounce rate of 9%, while pages that take 5 seconds to load have a bounce rate of 38%

Implementation tip: Use tools like Google PageSpeed Insights to identify specific speed optimization opportunities for your website.

2. Mobile Responsiveness

With mobile-first indexing, Google primarily uses the mobile version of a site’s content for ranking and indexing.

Implementation tip: Test your website across multiple devices and screen sizes, ensuring all functionality and content are accessible and properly displayed on smaller screens.

3. Intuitive Navigation and Site Structure

A logical site structure helps both users and search engines understand and navigate your content.

Implementation tip: Implement a clear hierarchical structure with breadcrumb navigation, keeping important pages within 3 clicks from the homepage.

4. Content Readability and Formatting

Well-structured, readable content satisfies both users and search engines:

  • Use descriptive headings and subheadings (H1, H2, H3)
  • Include bulleted and numbered lists for scannable content
  • Keep paragraphs short and focused (3-4 sentences maximum)
  • Use adequate white space to prevent content overwhelm

Implementation tip: Run content through readability tools to ensure it meets the appropriate reading level for your target audience.

5. Core Web Vitals Optimization


Google’s Core Web Vitals measure specific aspects of user experience:

Metric Measures Good Score
Largest Contentful Paint (LCP) Loading performance ≤ 2.5 seconds
First Input Delay (FID) Interactivity ≤ 100 milliseconds
Cumulative Layout Shift (CLS) Visual stability ≤ 0.1

Implementation tip: Use Google Search Console’s Core Web Vitals report to identify specific pages that need improvement.

How SEO Practices Enhance User Experience
The relationship works both ways—SEO practices can significantly improve user experience:

1. Keyword Research Reveals User Intent

Thorough keyword research uncovers what your audience is actually searching for, allowing you to create content that directly addresses their needs and questions.

User benefit: Visitors find exactly what they’re looking for, increasing satisfaction and engagement.

2. Content Optimization Improves Clarity

SEO content optimization requires clear structure, relevant headings, and concise meta descriptions.

User benefit: Content becomes more scannable, navigable, and useful to visitors.

3. Technical SEO Enhances Site Performance

Technical SEO improvements like fixing broken links, implementing proper redirects, and optimizing images directly improve user experience.

User benefit: Users encounter fewer errors and enjoy faster, more reliable site performance.

The Business Impact of Integrated UX and SEO

When Website UX and SEO work together, businesses see measurable improvements across key performance indicators:

Conversion Rate Optimization

Sites with strong UX and SEO integration typically experience higher conversion rates because:

  • Users find what they’re looking for more quickly
  • The path to conversion contains fewer obstacles
  • Content directly addresses user intent and pain points

Reduced Bounce Rates

When users land on pages that load quickly, display properly on their devices, and immediately address their search intent, they’re less likely to bounce back to search results.

Increased Time on Site

Engaging content that satisfies search intent, combined with intuitive navigation and relevant internal linking, encourages users to explore more of your website.

Higher Customer Satisfaction and Loyalty

Positive user experiences build trust and credibility, increasing the likelihood of return visits and brand loyalty.

Practical Strategies for Aligning UX and SEO

1. Conduct User Research Alongside Keyword Research

Implementation steps:

  • Create detailed user personas based on actual customer data
  • Map user journeys for each persona
  • Identify keywords and search terms relevant to each stage of the journey
  • Develop content that addresses specific user needs while targeting appropriate keywords

2. Design for User Goals While Incorporating SEO Elements

Implementation steps:

  • Structure page layouts around primary user goals
  • Incorporate keywords naturally into headlines, subheadings, and body text
  • Use schema markup to help search engines understand your content
  • Design clear calls-to-action that align with both user intent and business objectives

3. Prioritize Content Hierarchy for Both Humans and Search Engines

Implementation steps:

  • Implement logical heading structures (H1 → H2 → H3)
  • Front-load important information to satisfy both scanners and search engines
  • Use descriptive, keyword-rich anchor text for internal links
  • Create content clusters around pillar topics to establish topical authority

4. Measure and Optimize for Both UX and SEO Metrics

Develop a comprehensive dashboard that tracks metrics from both disciplines:

UX Metrics SEO Metrics Overlapping Metrics
Task completion rates Keyword rankings Bounce rate
User satisfaction scores Backlink quality/quantity Pages per session
Conversion funnel dropoffs Crawl statistics Average session duration
Usability test results Index coverage Mobile vs. desktop performance

Common Challenges and How to Overcome Them

Challenge 1: Balancing Keyword Optimization with Natural Content Flow

Solution: Focus on semantic relevance rather than exact keyword density. Use related terms, synonyms, and natural language that addresses the topic comprehensively.

Challenge 2: Reconciling Design Preferences with Technical Requirements

Solution: Establish collaborative workflows between design and SEO teams early in the process. Create shared guidelines that address both aesthetic and technical considerations.

Challenge 3: Maintaining Speed While Delivering Rich Experiences

Solution: Implement lazy loading for images and videos, use next-gen formats, and consider headless architecture to deliver fast, feature-rich experiences.

Challenge 4: Aligning Business Goals with User Expectations

Solution: Use data from both SEO and UX research to identify overlapping opportunities that satisfy both business objectives and user needs.

The Future of UX and SEO Integration

Looking ahead, several trends will further strengthen the relationship between UX and SEO:

  1. AI-Powered Search: As search engines employ more sophisticated AI, they’ll become even better at evaluating actual user satisfaction.
  2. Voice and Visual Search: These emerging search methods place even greater emphasis on understanding natural user behavior and intent.
  3. Personalization: Both UX and SEO will increasingly focus on delivering customized experiences based on user preferences and behaviors.
  4. Privacy-First Design: With the phasing out of third-party cookies, both disciplines will need to find new ways to understand and serve users while respecting their privacy.

Conclusion: A Unified Approach to Digital Success

The separation between UX and SEO is increasingly artificial. Today’s most successful websites treat them as complementary aspects of the same goal: connecting users with the content, products, and services they seek.

By aligning these disciplines, businesses can create a virtuous cycle: better user experiences lead to improved search rankings, which bring more visitors, providing more user data to further refine experiences. This integrated approach doesn’t just satisfy algorithms—it creates meaningful connections with the humans behind every search query.

Implementing a unified UX-SEO strategy requires cross-functional collaboration, a willingness to break down departmental silos, and a genuine commitment to serving user needs. The businesses that embrace this integrated approach will be best positioned to thrive in an increasingly competitive digital landscape.